Buy truewords.eu ?
We are moving the project
truewords.eu .
Are you interested in purchasing the domain
truewords.eu ?
domain@kv-gmbh.de · 0541-91531010
Buy truewords.eu ?
What is an alternative to iptables?
An alternative to iptables is nftables, which is a newer and more powerful packet filtering framework for Linux. Nftables provides a more user-friendly syntax and better performance compared to iptables. It also offers additional features such as stateful firewalling, easier rule management, and better integration with the Linux kernel. Overall, nftables is a modern replacement for iptables and is recommended for those looking for a more advanced and efficient packet filtering solution. **
Hello, I have a question regarding iptables.
Sure, I'd be happy to help. What specific question do you have about iptables? **

Similar search terms for Iptables
Top-Angebote
Products related to Iptables:
-
Sincere Surroundings Weatherproof Porch Board Welcome LeavesBold sage-green serif capitals spell out 'WELCOME' vertically down the length of this porch board, framed by delicate watercolor eucalyptus leaves and botanical sprays in soft sage and pale green tones that dance along both sides.42,99 $*Shipping: 0,00 $Secure redirect to the provider
-
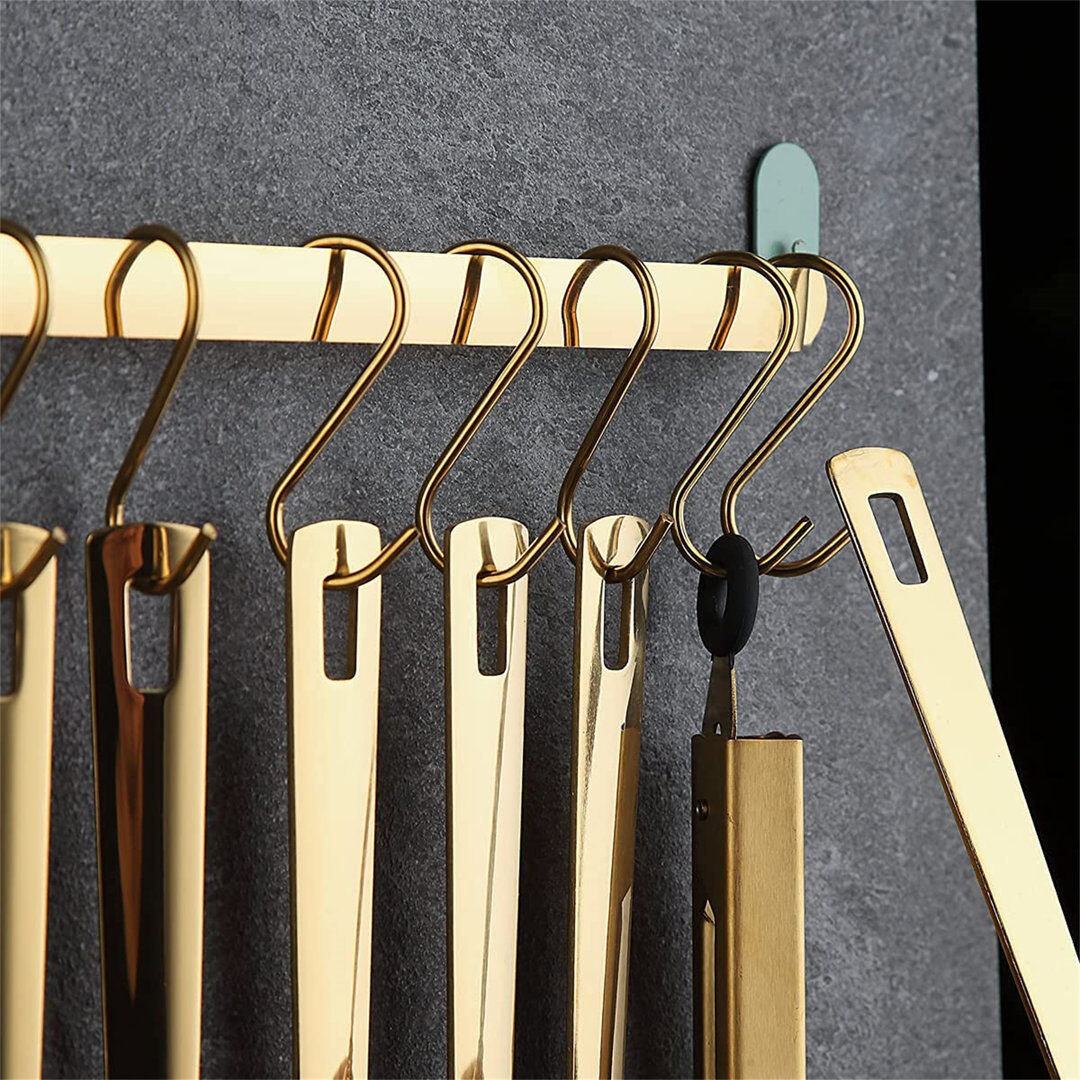
Belfry Kitchen Sincere 37 Utensil Set GoldDurable And Stylish Design: This cookware set is designed for functionality. The kitchen utensils are designed with high-grade stainless steel and plated with titanium gold, showing the noble luxury. It will elevate your kitchen decor. Healthy Materials: This cookware set is made of high-quality stainless steel, lead-free, PBA free, and suitable for everyday cooking. Best Kitchen Tools: A wide range of accessories to perfectly solve your culinary needs. It can be used not only at home but also in hotels, restaurants and other places. Quality materials and fine workmanship also make the perfect gift. Dishwasher Safe: The kitchen utensil set is made of high-quality stainless steel, which is durable and rust-resistant. Wipe clean and keep dry after use, use a soft cloth to clean and wash, do not use hard materials to wash and rub the utensils that keep it always shiny. It can last for years. Belfry Kitchen76,99 £*Shipping: 0,00 £Secure redirect to the provider
-
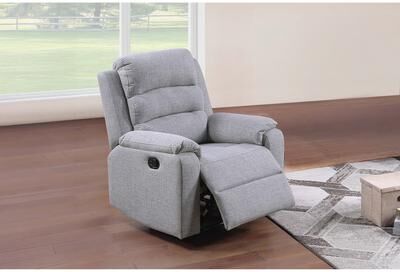
Esofastore Sincere Bone Finish 1pc Manual Recliner Tufted ChairFeatures:- •Transitioanl Style •Sincere Bone Finish •Burlap Fabric •Manual Sofa Set •Padded Headrest And Armrest •Manual Handle •Horizontal Tufting Product Description:- Indulge in unparalleled relaxation with the sofa set, crafted to deliver supreme…1266,99 $*Shipping: 0,00 $Secure redirect to the provider
-
How do I block everything except Tor with iptables?
To block everything except Tor with iptables, you can create a rule to allow traffic only through the Tor network. First, allow traffic to the Tor network by adding a rule to allow outbound traffic on the Tor port (usually 9050 or 9150) using the command: ```bash sudo iptables -A OUTPUT -p tcp --dport 9050 -j ACCEPT ``` Then, block all other outbound traffic by adding a rule to drop all other outgoing connections: ```bash sudo iptables -A OUTPUT -j DROP ``` This will ensure that all outbound traffic is blocked except for the traffic going through the Tor network. **
-
Why is the port not being allowed in iptables?
The port may not be allowed in iptables because the corresponding rule to allow traffic on that port may not have been added. This could be due to an oversight or mistake in configuring the iptables rules. Additionally, the port may be blocked by a default deny rule in iptables, which prevents any traffic from passing through unless specifically allowed. It's also possible that the service or application listening on that port is not running or is misconfigured, which would prevent iptables from allowing traffic to that port. **
-
How can I use iptables on the Asus RT-AC66U?
To use iptables on the Asus RT-AC66U, you can access the router's web interface by entering its IP address in a web browser. Once logged in, navigate to the "Administration" tab and then select "System" and "Enable JFFS custom scripts and configs." This will allow you to create custom iptables rules in the router's firewall script. You can then add your desired iptables rules to the firewall script to control network traffic according to your preferences. Remember to save your changes and reboot the router for the new rules to take effect. **
-
How can I block the SSH port from outside using iptables?
To block the SSH port (port 22) from outside using iptables, you can use the following command: ``` sudo iptables -A INPUT -p tcp --dport 22 -j DROP ``` This command adds a rule to the INPUT chain of iptables to drop any incoming TCP traffic on port 22, effectively blocking SSH access from outside. Make sure to save the iptables rules so they persist after a reboot by using the `iptables-save` command. Keep in mind that blocking the SSH port may lock you out of your server if you are not careful, so it's important to have an alternative way to access the server in case of any issues. **

What is the difference between honest and sincere?
Honesty refers to telling the truth and being straightforward in one's communication, while sincerity refers to being genuine and heartfelt in one's actions and expressions. In other words, honesty is about being truthful and transparent, while sincerity is about being genuine and authentic. One can be honest without being sincere, and vice versa. For example, someone can be honest about their feelings but not sincerely express them, or someone can sincerely express themselves but not be completely honest. **
Are there still honest, genuine people?
Yes, there are still honest and genuine people in the world. While it may sometimes seem like dishonesty and insincerity are prevalent, there are still many individuals who value honesty and authenticity in their interactions with others. These people can be found in all walks of life, and their integrity and genuineness can have a positive impact on those around them. It's important to recognize and appreciate these individuals and strive to embody those qualities ourselves. **
Top-Angebote
Products related to Iptables:
-
Sincere Surroundings Weatherproof Porch Boards Hide PackagesA witty welcome for the home where packages are a closely guarded secret, this porch board is designed to greet every delivery driver and guest at the front door with humor and charm.42,99 $*Shipping: 0,00 $Secure redirect to the provider
-
Sincere Surroundings Weatherproof Porch Board Welcome LeavesBold sage-green serif capitals spell out 'WELCOME' vertically down the length of this porch board, framed by delicate watercolor eucalyptus leaves and botanical sprays in soft sage and pale green tones that dance along both sides.42,99 $*Shipping: 0,00 $Secure redirect to the provider
-
What is an alternative to iptables?
An alternative to iptables is nftables, which is a newer and more powerful packet filtering framework for Linux. Nftables provides a more user-friendly syntax and better performance compared to iptables. It also offers additional features such as stateful firewalling, easier rule management, and better integration with the Linux kernel. Overall, nftables is a modern replacement for iptables and is recommended for those looking for a more advanced and efficient packet filtering solution. **
-
Hello, I have a question regarding iptables.
Sure, I'd be happy to help. What specific question do you have about iptables? **
-
How do I block everything except Tor with iptables?
To block everything except Tor with iptables, you can create a rule to allow traffic only through the Tor network. First, allow traffic to the Tor network by adding a rule to allow outbound traffic on the Tor port (usually 9050 or 9150) using the command: ```bash sudo iptables -A OUTPUT -p tcp --dport 9050 -j ACCEPT ``` Then, block all other outbound traffic by adding a rule to drop all other outgoing connections: ```bash sudo iptables -A OUTPUT -j DROP ``` This will ensure that all outbound traffic is blocked except for the traffic going through the Tor network. **
-
Why is the port not being allowed in iptables?
The port may not be allowed in iptables because the corresponding rule to allow traffic on that port may not have been added. This could be due to an oversight or mistake in configuring the iptables rules. Additionally, the port may be blocked by a default deny rule in iptables, which prevents any traffic from passing through unless specifically allowed. It's also possible that the service or application listening on that port is not running or is misconfigured, which would prevent iptables from allowing traffic to that port. **
Similar search terms for Iptables
-
Belfry Kitchen Sincere 37 Utensil Set GoldDurable And Stylish Design: This cookware set is designed for functionality. The kitchen utensils are designed with high-grade stainless steel and plated with titanium gold, showing the noble luxury. It will elevate your kitchen decor. Healthy Materials: This cookware set is made of high-quality stainless steel, lead-free, PBA free, and suitable for everyday cooking. Best Kitchen Tools: A wide range of accessories to perfectly solve your culinary needs. It can be used not only at home but also in hotels, restaurants and other places. Quality materials and fine workmanship also make the perfect gift. Dishwasher Safe: The kitchen utensil set is made of high-quality stainless steel, which is durable and rust-resistant. Wipe clean and keep dry after use, use a soft cloth to clean and wash, do not use hard materials to wash and rub the utensils that keep it always shiny. It can last for years. Belfry Kitchen76,99 £*Shipping: 0,00 £Secure redirect to the provider
-
Esofastore Sincere Bone Finish 1pc Manual Recliner Tufted ChairFeatures:- •Transitioanl Style •Sincere Bone Finish •Burlap Fabric •Manual Sofa Set •Padded Headrest And Armrest •Manual Handle •Horizontal Tufting Product Description:- Indulge in unparalleled relaxation with the sofa set, crafted to deliver supreme…1266,99 $*Shipping: 0,00 $Secure redirect to the provider
-
Sincere Surroundings Porch Board Weatherproof Peace On Earth Cardinal - 8x46.5x.5"Bring hope and holiday spirit to your entryway. Featuring the heartfelt sentiment, ""Peace On Earth,"" this weatherproof porch board welcomes guests with reflection and seasonal warmth."47,49 $*Shipping: 0,00 $Secure redirect to the provider
-
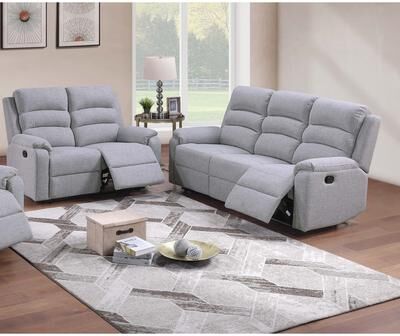
Esofastore Transitional 2pc Manual Sofa Set Burlap Upholstered Sincere Bone FinishFeatures:- •Transitioanl Style •Sincere Finish •Burlap Fabric •Manual Sofa Set •Padded Headrest And Armrest •Manual Handle •Horizontal Tufting Product Description:- Indulge in unparalleled relaxation with the sofa set, crafted to deliver supreme...2104,49 $*Shipping: 0,00 $Secure redirect to the provider
-
How can I use iptables on the Asus RT-AC66U?
To use iptables on the Asus RT-AC66U, you can access the router's web interface by entering its IP address in a web browser. Once logged in, navigate to the "Administration" tab and then select "System" and "Enable JFFS custom scripts and configs." This will allow you to create custom iptables rules in the router's firewall script. You can then add your desired iptables rules to the firewall script to control network traffic according to your preferences. Remember to save your changes and reboot the router for the new rules to take effect. **
-
How can I block the SSH port from outside using iptables?
To block the SSH port (port 22) from outside using iptables, you can use the following command: ``` sudo iptables -A INPUT -p tcp --dport 22 -j DROP ``` This command adds a rule to the INPUT chain of iptables to drop any incoming TCP traffic on port 22, effectively blocking SSH access from outside. Make sure to save the iptables rules so they persist after a reboot by using the `iptables-save` command. Keep in mind that blocking the SSH port may lock you out of your server if you are not careful, so it's important to have an alternative way to access the server in case of any issues. **
-
What is the difference between honest and sincere?
Honesty refers to telling the truth and being straightforward in one's communication, while sincerity refers to being genuine and heartfelt in one's actions and expressions. In other words, honesty is about being truthful and transparent, while sincerity is about being genuine and authentic. One can be honest without being sincere, and vice versa. For example, someone can be honest about their feelings but not sincerely express them, or someone can sincerely express themselves but not be completely honest. **
-
Are there still honest, genuine people?
Yes, there are still honest and genuine people in the world. While it may sometimes seem like dishonesty and insincerity are prevalent, there are still many individuals who value honesty and authenticity in their interactions with others. These people can be found in all walks of life, and their integrity and genuineness can have a positive impact on those around them. It's important to recognize and appreciate these individuals and strive to embody those qualities ourselves. **
* All prices are inclusive of VAT and, if applicable, plus shipping costs. The offer information is based on the details provided by the respective shop and is updated through automated processes. Real-time updates do not occur, so deviations can occur in individual cases. ** Note: Parts of this content were created by AI.